3.3.3 Robust Software (B04)
No description yet. This curated deck is ready for daily study.
Card preview (8)
what can go wrong when a program is executed? (4)
• user doesnt know what theyre doing - may select an incorrect option or supply an inappropriate input • data required by the program may become corrupted • a hardware fault may occur • a peripheral may not be available when required
robust software
code that can handle unexpected actions without crashing, generating incorrect output or revealing sensitive data.
code vulnerability
a flaw in a program which compromises security - can be exploited by an attacker to gain access to a computer system, enabling them to steal/corrupt data, introduce malware, take over control of the computer for some purpose of their own
language-specific vulnerabilities
a known flaw in a programming language which can pose a threat to security (eg C and Cplusplus programs can access memory which makes them a target for hackers who can use this as a ‘back door’ to introduce malicious code
bad programming practices (6)
• not having a properly thought through design • not sticking to agreed coding practices and standards (harder to integrate and less readable) • making do with a temporary fix for a problem (instead of finding a proper permanent solution • writing unstructured code instead of separating it into subprograms (harder to read and debug) • saving time using third party library modules without first checking that they are free from vulnerabilities • skimping on testing - without adequate testing, code is likely to be unreliable and error prone
code review (what are they done on, and 3 purposes)
done on working code spot instances of poor programming practice and find any vulnerabilties and check efficiency (3 things) used to minimise bad programming practices
2 types of code review
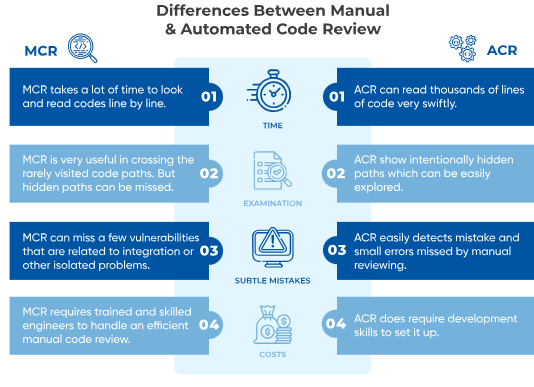
review by another programmer someone who is more senior and has more experience. reviewer will look through the code manually - labour intensive and time consuming automated review specialist piece of software used to examine the code - will highlight potential issues (vulnerabilities, terrible p.p.) - wont identify every issue but will flag up common and well-known problems
audit trail
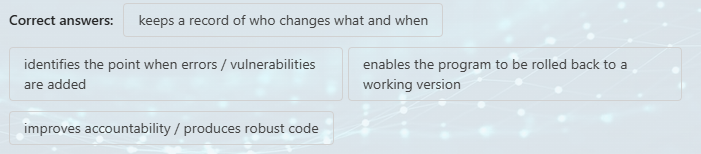
output from processes, documentation and automated software that identifies which person changed what code and when the change was made. reduces errors and improves accountability. if a security issue arises, it can be traced back to the version of the code when it first appeared. DOES NOT HELP YOU FIND BUGS